Reads every log line
Every machine in your fleet sends its logs to Sentinel, which looks for break-in attempts as they happen.
The security role: watches every log, locks out bad actors, brings in threat intel.
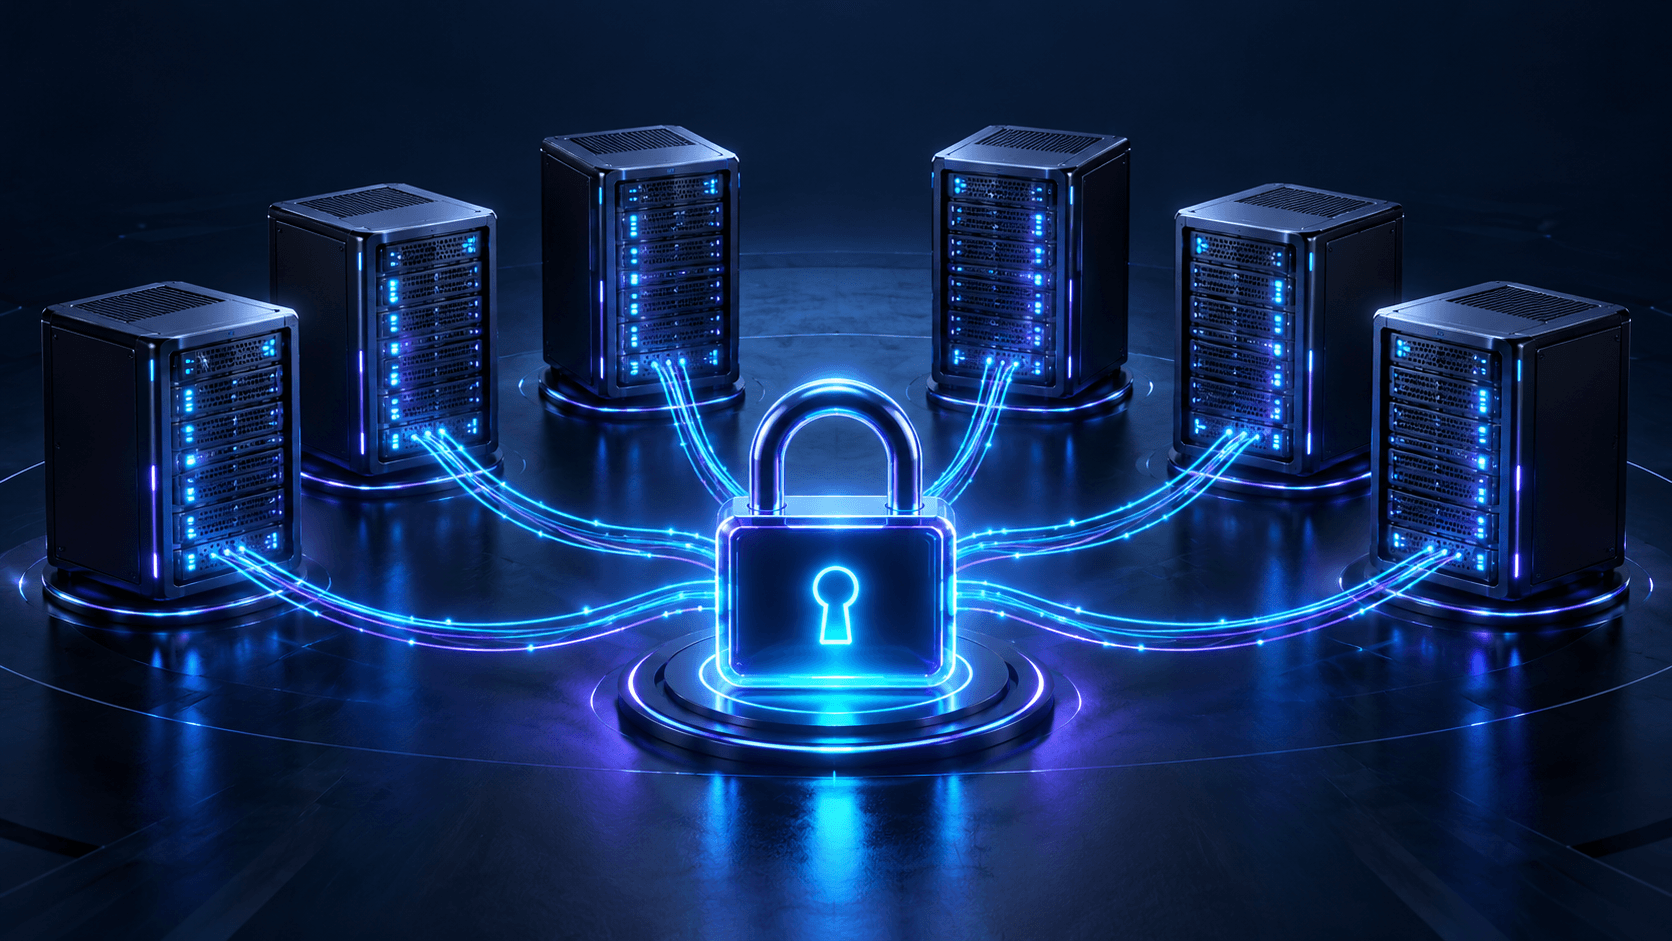
Every machine in your fleet sends its logs to Sentinel, which looks for break-in attempts as they happen.
When one address misbehaves on one machine, every machine in the fleet blocks it.
Shared threat lists block known bad addresses before they reach you.
Every fleet is different. We size each machine with you and help you source it from any vendor.
| Role | Security: log watching, fleet-wide lockouts, threat intel |
|---|---|
| Runs on | A machine you own, or one we help you choose and source |
| Needs | A dedicated machine, so security never competes with your apps |
| Works with | Gateway, Compute and Workshop |
| Managed by | Onyx, on the same screen as the rest of your fleet |
| Software | Onyx, set up in this role on your machine |
|---|---|
| Hardware | Yours. We help you choose and source it from any vendor, and you buy direct. |
| Managed service | Optional add-on: we watch and look after the machine for you |
The logs of every machine in your fleet, and network traffic for known attack patterns.
Its lockout service moves to another machine on its own. In a live test on our fleet that took 6 minutes, and every app kept its bans.
To pull in shared threat lists, yes. Watching and locking out work on your own network.